


Resilience is now part of the business model.
Financial institutions operate in an environment where cyber risk, operational risk and business risk are increasingly connected.
Cloud adoption and digital services expand the technology perimeter. Customers and employees expect secure access from anywhere. Third parties and technology providers become part of critical service delivery. Attackers target identities, data and financial processes, while regulatory requirements place greater emphasis on resilience, governance and the ability to respond and recover.
Financial institutions therefore need to protect not only their infrastructure, but also the continuity and trust on which their services are built.
What needs to stay secure.
Digital services
Customer-facing applications, platforms and digital channels.
Identities and access
Employees, customers, privileged users, third parties and machine identities.
Critical data
Sensitive financial and personal data across distributed environments.
Cloud and infrastructure
Hybrid and multi-cloud environments supporting critical services.
Third-party ecosystems
Providers, partners and interconnected services.
Business continuity
Critical financial services through disruption and recovery.
Cybersecurity priorities for financial services.
Strengthen operational resilience
Connect prevention, detection, response and recovery around critical business services and evolving risk.
Reduce exposure continuously
Identify and prioritize vulnerabilities, misconfigurations and attack paths according to their real potential impact.
Protect identity as the new perimeter
Strengthen identity governance, privileged access and authentication as users, workloads and services become increasingly distributed.
Secure cloud transformation
Bring security into cloud architecture, configuration, access, workloads and operations as financial services continue to modernize.
Validate defence against real attacks
Use offensive and purple-team techniques to test whether controls and detection capabilities work against realistic attack scenarios.
Turn regulatory requirements into operational capability
Connect governance, risk management and compliance with the security capabilities required to demonstrate and sustain resilience.
Relevant expertise for financial services
Different priorities require different combinations of cybersecurity capabilities.
Continuous security operations for financial services.
Financial environments do not stand still – and neither does their risk.
HyperSOC® brings together 24/7 expertise, technology, intelligence and automation to continuously understand risk and exposure, prioritize action, detect and respond to threats, and improve security outcomes.
Integrated into the customer's cybersecurity operating model, it enables managed security capabilities to evolve alongside the institution's environment, priorities and risk tolerance.
Proven in regulated environments.
HWG Sababa works with organizations operating in complex and regulated environments, combining continuous security operations with specialist capabilities across cloud, identity, exposure management, offensive security and resilience.
Customer story
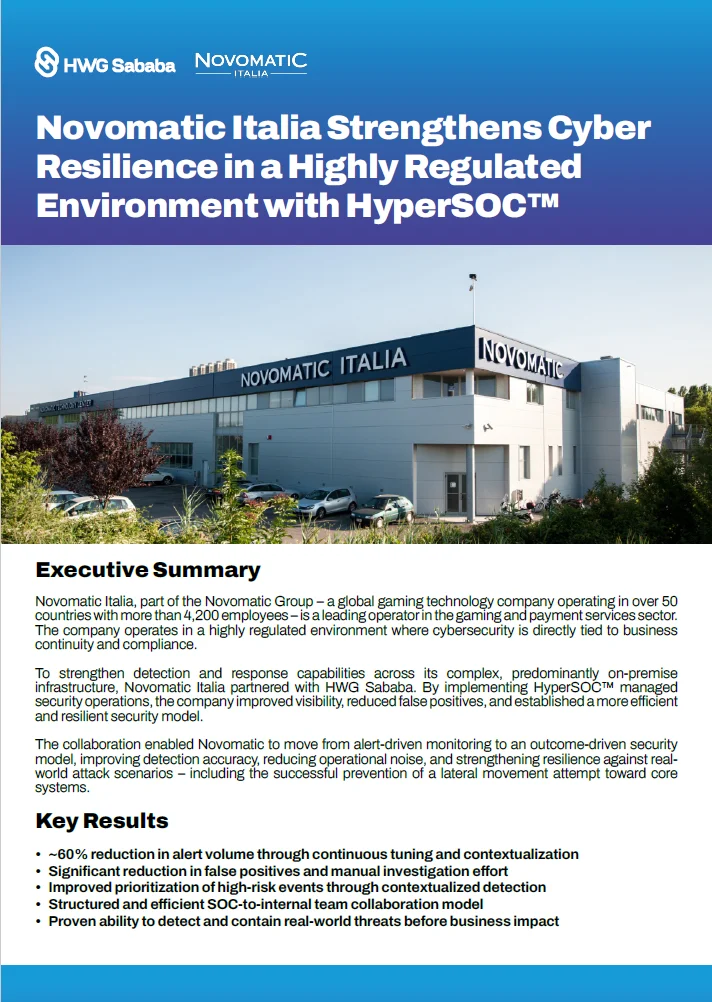
HyperSOC™ – Novomatic
Novomatic Italia, part of the Novomatic Group – a global gaming technology company operating in over 50 countries with more than 4,200 employees – is…
Customer story
Awareness for Ravnaq Bank
Remaining among the major cyberthreats in Europe, phishing is also a big deal for businesses in the Central Asian countries. Training their employees nd empower…