


Having detections does not mean they work.
Security environments change continuously. Log sources, configurations, technologies and detection rules evolve – and so do attacker techniques.
A rule may exist but fail to trigger. A change in a log source can silently break detection. Coverage may look complete on paper without ever being tested against realistic attacker behaviour.
Purple Teaming provides objective evidence of what the defence can actually detect and respond to – and turns identified gaps into direct improvements.
Assess. Engineer. Validate. Improve.
Assess defensive capability
Review SOC people, processes and technology, including log-source quality, detection coverage, triage and response processes.
Engineer better detections
Build and optimize detection logic for the customer environment, informed by threat intelligence and supported by response playbooks.
Validate what works
Test detection use cases and security controls through controlled attack simulation and security validation – across the wider security stack, not only the SIEM.
Identify and prioritize gaps
Understand where detections, controls or operational processes fail and create a prioritized improvement backlog with clear ownership.
Retest and improve
Validate changes, track coverage over time and feed lessons back into security operations.
Make defensive validation continuous.
Purple Teaming creates a closed feedback loop between testing and security operations.
Defensive capability is assessed, detections are engineered around relevant threats, controls and use cases are validated, and identified gaps are improved and tested again.
Through HyperSOC®, detection engineering, threat intelligence, validation and security operations can work within the same operating model – turning validation results into stronger detection, response and threat hunting.
Turn security coverage into evidence.
Expose defensive blind spots
Identify where detection rules, controls or operational processes fail against relevant attacker behaviour.
Improve detection quality
Build and tune detection logic based on validated techniques and observed gaps.
Validate security investments
Understand whether deployed security technologies and controls perform as expected.
Strengthen security operations
Improve detection coverage, investigation and response based on evidence from validation.
Track improvement over time
Retest changes and measure how defensive coverage evolves rather than relying on a one-off assessment.
Purple Teaming in practice.
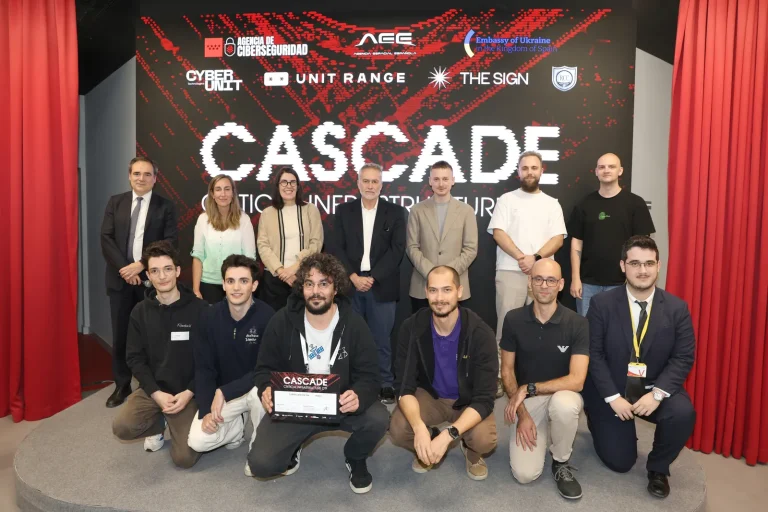
CASCADE Hackathon 2026: second place
HWG Sababa’s Offensive team took second place at the CASCADE – Critical Infrastructure CTF hackathon in Madrid, built on realistic attacks against critical infrastructure.