


The Post-Alert SOC: How AI Is Reshaping MDR
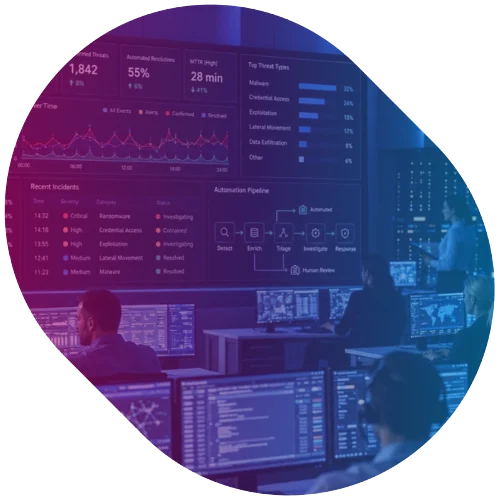
The Post-Alert SOC: How AI Is Reshaping MDR For years, Managed Detection and Response (MDR) has helped organizations address a fundamental security operations challenge: how to manage increasingly complex environments, growing volumes of telemetry and an overwhelming number of alerts around the clock. AI begins to change that equation. Triage, enrichment, case building and parts […]
AI SOC Agents: The Next Evolution of Security Operations
AI SOC Agents: What Exactly Are We Talking About? Artificial intelligence has fundamentally changed the economics of cyberattacks. Tasks that once required highly specialized expertise – reconnaissance, phishing, malware development, and attack planning – can now be completed faster, at greater scale, and by less experienced threat actors. As attackers accelerate, Security Operations Centers (SOCs) […]
SOC Platform Management: Why Continuity Demands More Than Just Integration
HyperSOC™ transforms SOC platform management from fragmented tool oversight into a resilient, unified operating system. Built for hybrid IT/OT environments, it configures and orchestrates all onboarded technologies, normalizes telemetry in real time, and delivers continuous performance, faster response, and audit-ready visibility – empowering CISOs to move from reactive workflows to proactive, business-aligned security operations. As […]
HyperSOC™ Delivers Real-Time SOC Threat Context That Powers Proactive Defense
HyperSOC™ delivers real-time SOC threat context by enriching raw threat data with internal telemetry and business relevance. This approach filters noise, prioritizes risks, and enables smarter, faster decisions. Instead of reacting blindly, analysts act on actionable intelligence – reducing false positives, improving MTTR, and aligning SOC operations with risk management. Context isn’t optional – it’s […]
HyperSOC™: Real-Time SOC Data Enrichment for Decisive Action
In modern cybersecurity, data isn’t just raw input – it’s operational intelligence. Yet many Security Operations Centers (SOCs) remain burdened by fragmented, inconsistent telemetry that hinders decision-making. The result? Delayed triage, alert fatigue, and reactive postures. HyperSOC™ changes the game by turning SOC data enrichment into a real-time engine for clarity, precision, and speed. Why […]
Why SOC Compliance is No Longer Optional – And How HyperSOC™ Embeds It by Design
SOC compliance is no longer optional – it’s essential for cyber resilience. HyperSOC™ embeds compliance into its core, aligning with frameworks like NIS2, DORA, ISO 27001, and IEC 62443. With built-in telemetry normalization, audit readiness, and compliance-aware orchestration, it enables real-time accountability, faster response, and continuous alignment – transforming compliance from burden to strategic advantage. […]
HyperSOC: The Power of SOC Hyperautomation at Machine Speed
In cybersecurity, speed is no longer an advantage – it is the baseline. Threats are faster, more coordinated, and increasingly automated. For traditional Security Operations Centers (SOCs), this has exposed a critical flaw: manual response cannot keep pace with machine-speed threats. Enter SOC hyperautomation – the strategic combination of AI and automation that turns a […]
Why the Future-Proof SOC is the New Standard for 2025 Security Leaders
Traditional SOCs can’t keep up with today’s speed, scale, and complexity. The future-proof SOC is now the 2025 standard – built on five pillars: compliance, data, platform, threat intelligence, and AI. HyperSOC delivers this model as a unified, resilient, and scalable platform that powers proactive, governance-aligned security operations at machine speed. Security operations are under […]
Why 2025 CISOs Can’t Afford Static SOCs?
Static SOCs can’t keep up with 2025’s AI-driven threat landscape. With rigid playbooks, fragmented tooling, and manual triage, they expose organizations to breaches, downtime, and compliance failures. HyperSOC™ eliminates static SOC risks with AI-powered detection and response, modular architecture, real-time telemetry enrichment, and compliance by design – delivering the speed, visibility, and resilience modern CISOs […]
From Signal to Insight: Why Observability Is the Future of Cybersecurity
In cybersecurity, visibility is the starting line – not the finish. And as enterprise infrastructures sprawl across cloud, on-prem, remote, and hybrid domains, traditional monitoring systems, though still essential, are no longer enough. Enter observability – the evolution of monitoring that’s reshaping how security teams detect, interpret, and act on cyber threats. If monitoring tells […]