
The Post-Alert SOC: How AI Is Reshaping MDR
For years, Managed Detection and Response (MDR) has helped organizations address a fundamental security operations challenge: how to manage increasingly complex environments, growing volumes of telemetry and an overwhelming number of alerts around the clock.
AI begins to change that equation. Triage, enrichment, case building and parts of investigation can increasingly be automated or augmented by AI. But this does not make managed security less relevant. It shifts the value organizations seek from MDR: from handling alerts toward engineering and continuously improving the security operation itself.
From alert processing to detection engineering
A traditional SOC workflow starts when something happens: an alert is generated, enriched, prioritized and investigated. Automation has already compressed this cycle, and AI will accelerate it further.
But a modern security operation cannot be measured only by how efficiently it processes what the security stack produces. It also needs to determine what should be detected, why it matters and what should happen next.
This is where detection becomes an engineering discipline. Every organization has a different infrastructure, attack surface and risk profile. Effective detection therefore requires continuous decisions: Which attacker behaviours matter most? Do we have the telemetry to identify them? Where are the blind spots? Which processes can be automated safely? How should confirmed threats trigger response?
AI can support this work, but it does not remove the need for expertise. Instead, human roles increasingly shift toward more in-depth activities such as detection engineering, automation oversight, complex investigation and continuous improvement.
Detection needs context
Engineering better detections is only part of the shift. An alert can tell us that something happened, but not necessarily how much it matters. Two technically identical vulnerabilities can represent very different risks depending on the affected asset, its exposure, business criticality and potential role in an attack path.
This is why exposure management is increasingly becoming part of continuous security operations. Bringing Continuous Threat Exposure Management (CTEM) closer to detection and response helps connect what could be attacked with what is actually happening in the environment.
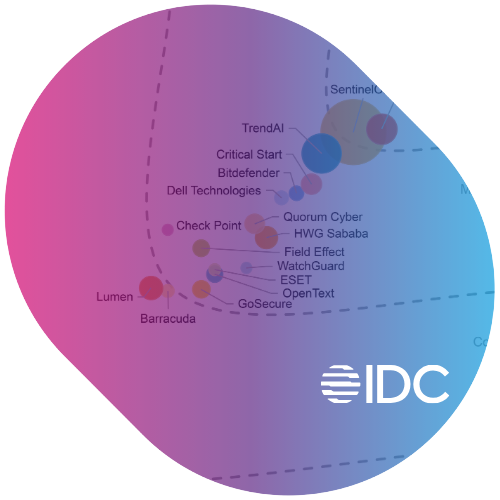
IDC identifies this convergence as one of the forces reshaping MDR, observing that leading providers are bringing “vulnerability intelligence, attack surface data, and asset criticality context directly into the investigation workflow.” The result is faster and more accurate severity assessment and a shift toward continuous risk reduction rather than incident response alone.
Combining asset, identity, exposure, threat and business context allows security teams to prioritize what genuinely requires attention. More importantly, that context can feed back into detection and preventive controls before an incident develops, shifting security operations from reactive response toward proactive defence.
Speed makes integration critical
At the same time, the pace of attacks is accelerating. AI and automation can reduce the effort required for reconnaissance across IT and OT environments and automate parts of attack execution, while modern ransomware operations can move from initial access to data exfiltration within hours.
Defensive automation is therefore essential, but automating isolated tasks is not enough. Detection, enrichment, investigation, decision and response need to operate as a connected cycle, with each outcome informing and improving what happens next.
The goal is not simply faster alert processing, but a shorter, smarter cycle between detection, understanding, decision and response.
So what becomes of MDR?
What organizations expect from their managed security providers is changing. 24/7 monitoring remains essential, but the focus is expanding toward continuously improving how the environment is defended.
That requires technology expertise, detection engineering, threat and exposure intelligence, automation, investigation and response to work together within the customer’s security operating model.
At HWG Sababa, this is the direction behind HyperSOC®: connecting people, technology, intelligence and automation into a continuous security process.
As AI makes alert processing increasingly scalable, access to the technology itself will not differentiate MDR providers. What matters is how effectively it is engineered into security operations – and whether it delivers better security outcomes over time.
The future of MDR is therefore broader than monitoring security. It is the shift from responding to what happens to continuously improving how security operates.